By SDCN Staff
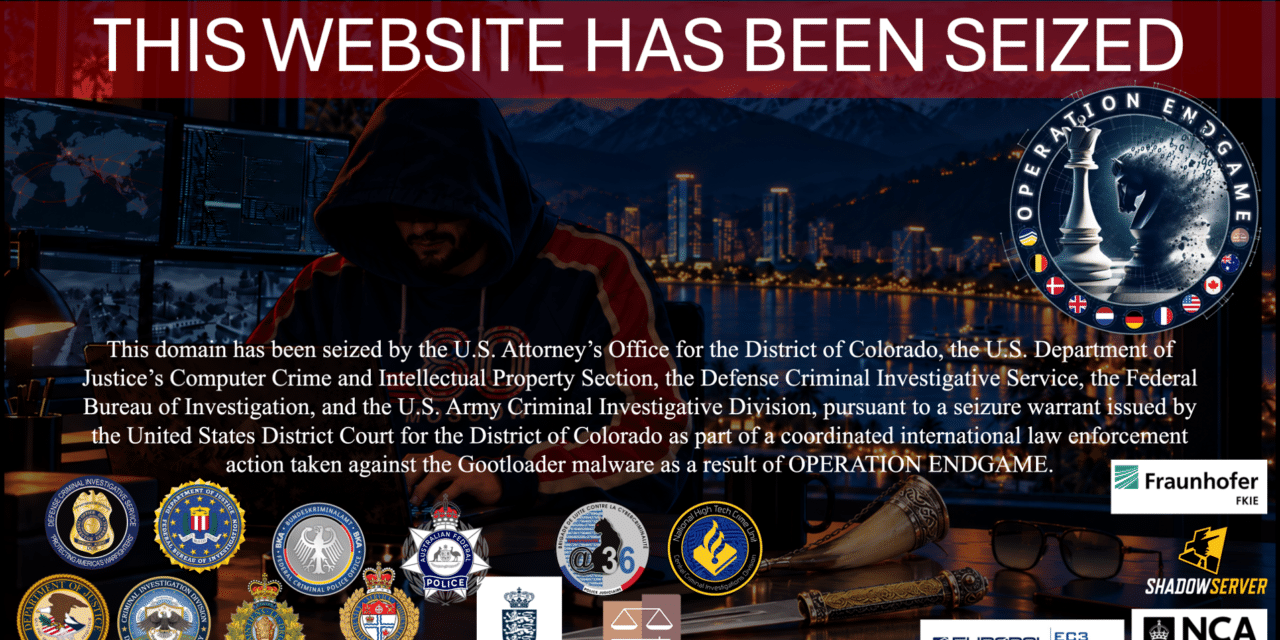
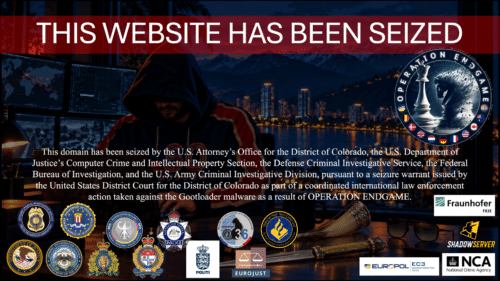
Washington, D.C.–Federal authorities announced Thursday the successful removal of malware known as “Gootloader” from over 100 computer servers, including compromised WordPress sites, and the seizure of U.S. domain names used by criminals to deliver and control the Gootloader malware.
Since 2018, Gootloader malware has infected at least 25,000 computers around the world. Gootloader malware has been used in ransomware attacks on at least 44 U.S.-based victims, resulting in approximately $28.8 million in loss.
“With court authorization, the Department of Justice and FBI, along with our international partners, conducted an online operation that liberated over 100 servers from malicious software, denying ransomware criminals a platform,” said Assistant Attorney General A.Tysen Duva of the Justice Department’s Criminal Division.
According to warrants unsealed this week, Gootloader is malware that infects victim computers through a variety of means, often by tricking unsuspecting individuals into downloading it. Once infected, the compromised computers are added to a network of other compromised computers known as a botnet. The actors behind Gootloader used the botnet to infect other computers, then sell access to those later-infected computers to ransomware actors.
In addition to the law enforcement seizures, the Shadowserver Foundation assisted by working with internet service providers and Computer Security Incident Response Teams to identify infected systems, aid in notifying victims, and assist in remediation.
The actions were conducted in coordination with Operation Endgame, a multinational law enforcement initiative targeting the dismantling of malware cybercriminal services.
The Gootloader investigation was led by DCIS, FBI’s Denver Field Office and the Army Criminal Investigative Division, working closely with Germany’s Bundeskriminalamt, the Netherlands National Police’s National High Tech Crime Unit, Canada’s Royal Canadian Mounted Police and Ottawa Police Service, Danish Police, Brigade de Lutte contre la cybercriminalité (Paris Cybercrime Unit), United Kingdom’s National Crime Agency, the Australian Federal Police and Europol. ICHIP the Hague, Fraunhofer FKIE, Registrar of Last Resort, OpenAI and Sharktech, Inc. also provided valuable technical assistance to the investigation.
Senior Counsel Thomas Dougherty of the Criminal Division’s Computer Crime and Intellectual Property Section, and Assistant U.S. Attorney Jasand Mock for the District of Colorado are prosecuting the case. The Justice Department’s Office of International Affairs also provided valuable assistance.